Operational
We assess whether processes run correctly and consistently by examining workflows, segregation of duties, approvals, inventory and resource use.
SARUS AREAS OF EXPERTISE
We make risks visible, controls effective and outcomes traceable.
Together, we assess your organisation's risks and control needs, then build a practical, sustainable internal audit and control system with clear responsibilities.
Our aim is to build a structure that identifies risks early, directs resources to priority areas and supports management decisions with reliable information. We design controls around your organisation's size, operations and risk profile, and embed them in everyday processes.
From needs to a working system
We take a comprehensive view of your control framework through five workstreams, from the roadmap to regular monitoring.
We assess the current structure and clarify priority risks, control objectives and improvement actions, with defined owners and timelines.
We map process risks to controls and define control owners, frequency and evidence, making missing or inadequate controls visible.
We plan the audit scope, priorities and methods around your risk profile, then assess the design and operating effectiveness of existing controls.
We prepare easy-to-use checklists that support regular, consistent and verifiable control activities in critical processes.
Using ERP, Excel and other data sources, we create indicators, alerts and monitoring reports that help identify deviations and exceptions early.
Areas we assess together
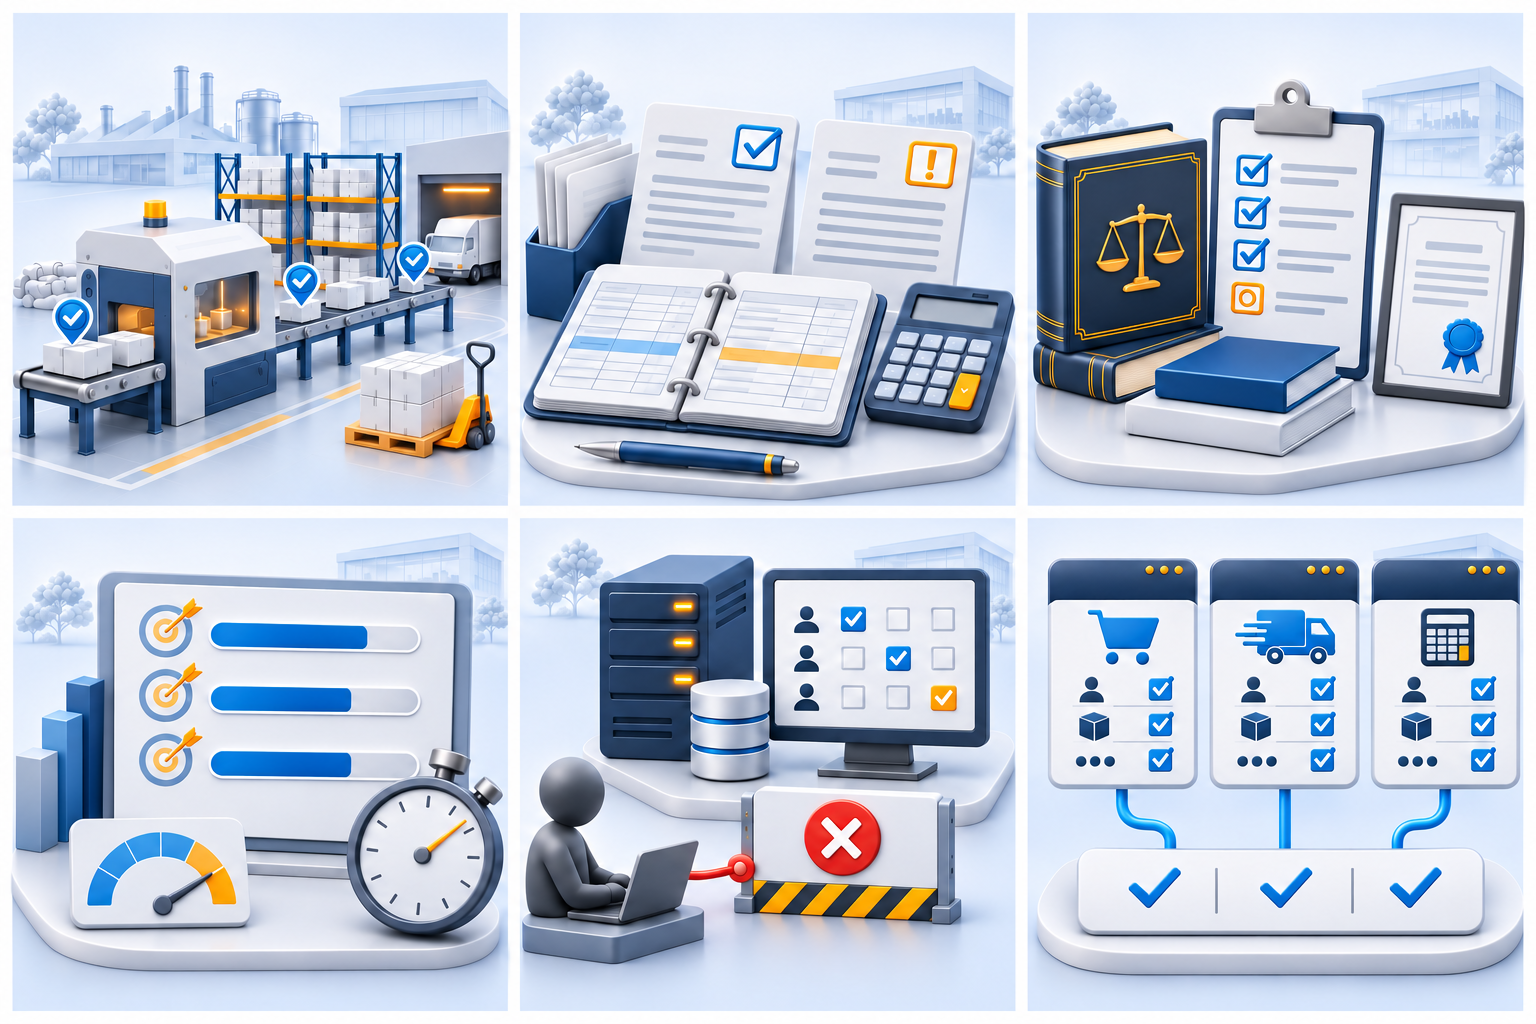
From operations to information systems, we examine how processes affect one another and how consistently their records align.
We assess whether processes run correctly and consistently by examining workflows, segregation of duties, approvals, inventory and resource use.
We examine accuracy, completeness and traceability in accounting records, reconciliations, collections, payments and financial reporting.
We assess whether activities comply with applicable regulations, organisational policies, procedures and contractual obligations.
We track targets and actual results alongside efficiency, cost, quality and timing indicators to examine the causes of deviations.
We examine user permissions, access restrictions, transaction logs and data security controls.
We compare customer, product, quantity and amount information across sales, dispatch and accounting to identify missing, duplicate or inconsistent records.
How we work
We do more than deliver a report. We build a system that works.
Together, we define the processes, risks, existing controls and management's assurance needs.
We establish the roadmap, risk and control matrix, audit programme and responsibilities.
We put checklists, audit activities and data-based monitoring tools into practice.
We turn findings into actions and monitor progress and the effectiveness of improvements.
Each finding has a defined owner, target date and verification step. Management and process owners are responsible for owning and implementing controls; internal audit assesses their effectiveness.
Let's clarify together
For an initial assessment, it is enough to share your company's business activities, organisational structure, systems and priority risk and control needs.
Yes. We assess your existing data sources, reports and control methods. We retain what is usable and develop practical solutions for missing control points and monitoring needs.
Findings are turned into actions with defined owners, target dates and priorities. Progress is monitored, and the effectiveness of actions reported as complete is verified.
Let's get started together
Share your needs, and together we will define the priorities, scope and first step.